Preface
Actually, while working on hcaptcha challenge, I kept wondering: what will the next generation of CAPTCHA look like? What will the development path of CAPTCHA be?
Where is the Next Generation of CAPTCHA? The History of CAPTCHA? Human-Machine Confrontation? What Will the Next Generation of CAPTCHA Look Like?
Origins
In the early days of the internet, many people used Leet Code1 to bypass keyword filtering.
In 2000, idrive.com began using CAPTCHA to protect its registration page; this was the first generation of CAPTCHA.
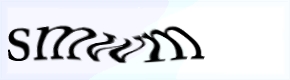
Before machine learning, especially deep learning, became widely adopted, the simplest way to handle this type of CAPTCHA was “crowdsourcing.” Images were sent to the server, which then distributed tasks to workers. This was the original “code-breaking platform.” Have you ever tried it? I encountered the term “code-breaking platform” back in middle school, and it might even have been my first pot of gold (?)—though I can’t remember for sure. Back then, the price per CAPTCHA was likely just a few cents. For an hour of work, you might earn about 1 yuan. Skilled workers could earn over 20 yuan a day. Some people treated it as typing practice hhh, and I approached it with the same mindset.
Later, Optical Character Recognition (OCR) emerged to counter these CAPTCHAs. While this is very common now, in the early days when OCR technology was immature, few people attempted it. Defeating the early OCR was quite easy: just add some noise or a horizontal line, and it would fail. Consequently, the industry reverted to the “crowdsourcing” model.
Later still, many image-based CAPTCHAs appeared in the form of math problems, requiring not only accurate character recognition but also an additional calculation step.
Diverse Forms of CAPTCHA
Nowadays, CAPTCHAs based on image character recognition have become less common after being cracked by OCR. They have been replaced by a wide variety of other CAPTCHA formats.
For example, click on the objects in the image in sequence. The characters may be tilted or distorted, and colors may vary. This requires OCR to have high robustness, and the data returned is simply click coordinates.
There are also CAPTCHAs that have evolved from text to icons or graphics. The underlying logic remains the same, but instead of text recognition, it has become an image matching problem.
Then there are slider CAPTCHAs, where you simply drag the slider from left to right. The difficulty lies in the need to hold the slider down rather than just clicking the screen, and the sliding speed should not be constant.
There is also an improved version of the slider CAPTCHA: the puzzle CAPTCHA. For instance, GeeTest uses a puzzle CAPTCHA that adds a puzzle piece from the top image to the slider mechanism. There may be distractors, such as a completely unrelated puzzle piece suddenly appearing darkened in the image.
Image Recognition
Furthermore, we reached the era of advanced reCAPTCHA, which shifted the requirement to image recognition or object detection, asking you to select images containing buses or crosswalks. These CAPTCHAs have sparked a lot of complaints. Often, users feel they selected everything correctly but still fail verification. Sometimes, you are forced to click many times, and there are even response time limits. This has not only caused widespread dissatisfaction but also made many people question whether they are actually human hhhh.
However, once a sufficient dataset is collected, the emergence of YOLOv5, with its high speed and lightweight performance, quickly became the nemesis of this type of CAPTCHA.
hCAPTCHA also joined this battle and captured a significant market share. Recently, hCAPTCHA’s CAPTCHA upgrades truly caught my eye (e.g., vertical river, sky left airplant, elephant drawn with leaves). By incorporating Generative Adversarial Networks (GANs) into CAPTCHAs, they provide an infinite supply of data. But when I solved them using a simpler method ([1]2[2]3[3]4), I couldn’t help but question their very existence.
The Next Generation of CAPTCHA
An interesting fact is that while CAPTCHA protects websites from attacks, the websites providing CAPTCHA are essentially running naked.
Crawling the data from these “naked” CAPTCHAs is incredibly simple. For a 9-grid CAPTCHA, it is essentially a binary classification task because you only have two choices: click or don’t click. Moreover, due to the inherent limitations of CAPTCHA, high-resolution images cannot be used. This means the model can be as small as possible, and the image features will be very obvious.
When an adversary keeps up with the frequency of CAPTCHA updates, it becomes terrifying. For every new task that appears, the adversary only needs less than one day to complete data labeling and model training.
This makes one wonder: if a CAPTCHA algorithm engineer spends over half a month creating a Generative Adversarial Network ready for production deployment, and an adversary completes data labeling and model training in less than a day, is it really worth it?
Furthermore, the ultimate goal of CAPTCHA is to serve humans. If it degrades the user experience, is that a good outcome?
Regarding the next generation of CAPTCHA, I would like to discuss it from two aspects:
Image-based
Will this kind of CAPTCHA have a future? (After all, everyone should be clear about how fiercely competitive the CV field in deep learning has become.) However, temporary use can still be effective. For instance, you could use results rendered in 3D to test a model’s 3D understanding capabilities. Currently, 3D understanding remains somewhat challenging, among other things.
Simplify the Complex - CAPTCHA-less
reCAPTCHA is already trying this, which is likely the mainstream direction for the next generation of CAPTCHAs. By monitoring the environment at the browser or system level to assess the probability of a malicious user, and combining this with user behavior to build a multimodal model, we can not only optimize the user experience (since users won’t even notice the CAPTCHA appearing) but also intercept malicious programs.
Reference
Sources: 5.

